Global — Ekhbary News Agency
Hackers are actively compromising websites running vulnerable versions of WordPress, a situation cybersecurity firms describe as critical. Tens of millions of WordPress websites likely remain susceptible to these attacks as of Monday, for what it's worth, despite recent urgent patches. The popular blogging software last week addressed two critical security flaws, prompting an immediate update directive for all users.
Widespread Exploitation Confirmed
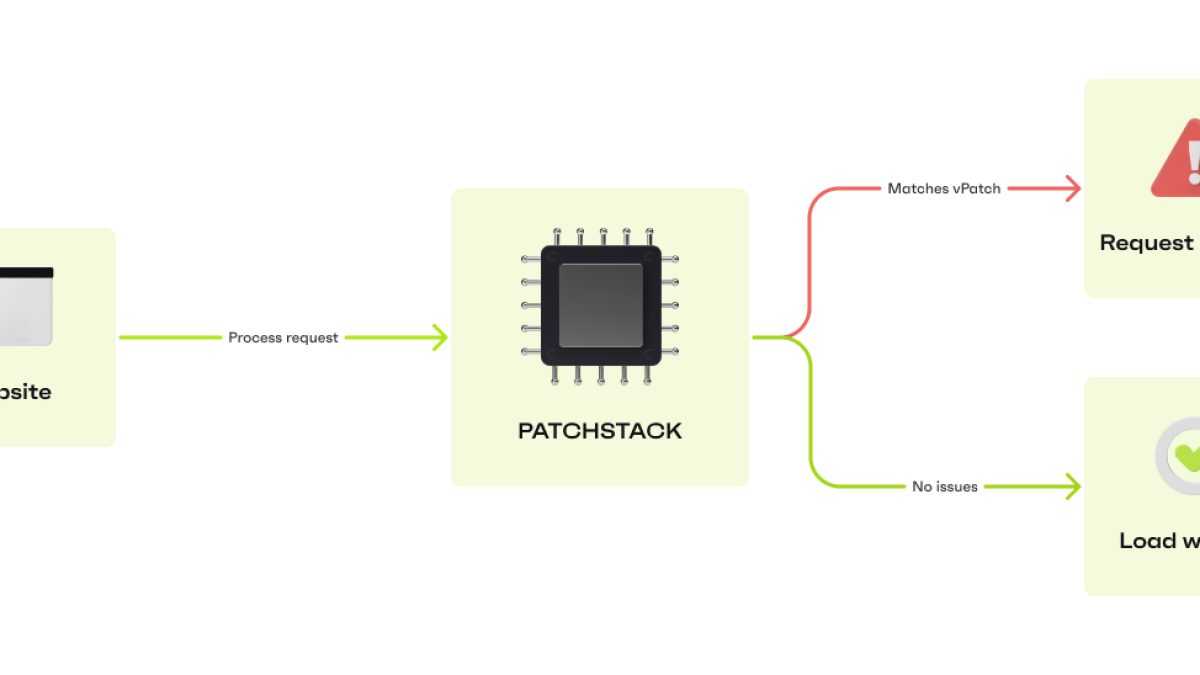
Following WordPress's release of patches, which included forced updates where technically feasible, cybersecurity companies like Patchstack, Hexastrike, and WatchTowr have issued warnings. Their collective intelligence confirms that malicious actors are exploiting these vulnerabilities "in the wild," meaning they are successfully taking over unpatched websites. The sheer scale of potential compromise remains a significant concern for web administrators globally.
read_also
- Oukitel WP210: A Balanced Rugged Phone Tested for Durability
- Quantum-Resistant USB Drive Tested: High Security Without Extreme Cost
- ZDNET Details Independent Review Process for Product Recommendations
- India's First Private Rocket Vikram-1 Achieves Orbit on Debut Launch
- AI Coding Harnesses: Lean vs. Structured Context Approaches Emerge
Estimates on Vulnerable Sites Vary
While WordPress's official statistics suggest over 400 million sites run flawed versions (6.9.0-6.9.4 and 7.0.0-7.0.1), these figures may not reflect recent updates. Cybersecurity consultant Daniel Card, examining a sample of 3,500 WordPress sites, estimates less than 15% are currently vulnerable. Projecting this across the internet's total WordPress population still suggests approximately 90 million sites could be at risk. Automattic, through spokesperson Megan Fox, affirmed that all sites hosted by their services were protected even before the public patch release, deploying updates immediately across millions of sites once available. This proactive defense highlights the ongoing race between developers and attackers.